Threat Intel

Vulnerabilities in PHP (CVE-2026-109618 / CVE-2026-109619)

Another day, another vulnerability, as has been so… for basically forever. However if you run PHP you don’t want to sleep on this one, due to some shenanigans there’s been an ‘early release of intel’ (leak) and a patch for PHP is on the way, however there’s also now a PoC in the wild! But the devil, as always is in the details! So let’s explore those, as always this is a fast publish and you should look to the vendor for guidance etc. with that important caveat aside, let’s explore:

Read more “Vulnerabilities in PHP (CVE-2026-109618 / CVE-2026-109619)” →
Defense

Creating a honeypot for CVE-2021-41773 (Path Traversal and RCE)

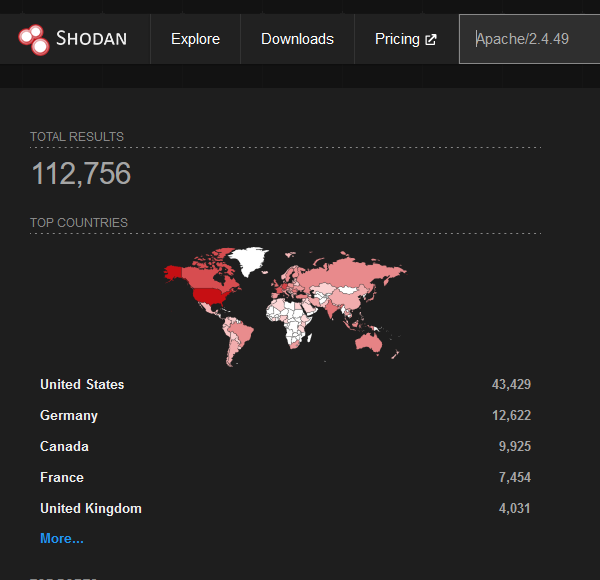
A path traversal vulnerability and exploit just dropped in the wild for a specific version of Apache (Apache/2.4.49). This vulnerability allows an unauthenticated attacker to execute a path traversal attack (and now shown RCE if MOD_CGI is enabled) to read files outside of the virtual directory path bounds. This only affects a single version of Apache, there’s a fair few of these online, however it’s very unlikely all are vulnerable. The vulnerability requires specific permissions to be configured.

A screenshot of a video game

Description automatically generated with medium confidence

Read more “Creating a honeypot for CVE-2021-41773 (Path Traversal and RCE)” →