Leadership

You Can’t Defend Everything: Threat Modelling as an Economics…

In a world now seemingly filled with mad probability robots you might think this makes the world simpler, I’m not so sure…. More code, faster, more tools, faster, more technical debt, faster… and then what of the erosion of the human importance? Well human 2.0 is probably augmented not redundant… and who doesn’t love a bit of Deus Ex! Now full disclosure this blog is guided by me but written by Claude (mostly), why? Why not? I’m still here, guiding things, writing this intro by hand, but the concepts of cyber security, the foundations and underpinning logic, well they are probably older than me! I’m not talking about castles and moats, but even they play a part in our understanding of attack and defence. There’s even a bit of a public wifi link here if you read between the lines. Not every threat actors is all knowing and all powerful (in fact no one is!). So let’s see what Claude Opus 4.8 has to say about the topic:

Read more “You Can’t Defend Everything: Threat Modelling as an Economics Problem” →
Threat Intel

Bleeding Out

When you compromise a firewall you have lots of options in terms of next steps, from using the VPN, changing configurations, creating backdoors or perhaps using the firewall to PCAP. In this post I’m going to explore the ‘Fortibleed’ campaign. I have to note, we can see in honeypot logs this TA did not seem to limit themselves to Fortinet exploitation, however the area of analysis has a heavy Fortinet element. You will see they deployed a capture and analysis platform. Treat everything with a pinch of salt because I’m using a mad probability based machine (LLM) to support me for this!

Read more “Bleeding Out” →
Threat Intel

Fortibleed

In the ‘world of Mythos’ and other such overhyped AI buzz words…. the fundamentals of digital security still apply. Don’t get me wrong, I think LLMs are great, as a digital defender, I’ve been using LLMs relatively for a long time now (from offence to defence to general CTI/Research) so I’m not a hater, they are like an Iron Man suit! But we still need our Tony Stark and Pepper Potts!

It’s very easy in a world full of complexity to oversimplify, it’s very easy to focus on one class of threat and ignore another. Zero days sound cool, when mass exploration occurs, it’s a real problem, but for the day to day in an org, authentication attacks (identity plane) are the number one thing you will likely be seeing (if you look at our logs… you have logs right???)

Read more “Fortibleed” →
Leadership

Cyber Myth: Attackers only have to be right once,…

Our cyber world is full of myths and FUD:

Attackers only have to be right once, Defenders have to be right all the time!

Firstly, let’s cut straight to the chase, I can only assume that someone who says this is ignoring or is unaware of how computer systems and intrusions work. But surely this is a true phrase, I’ve seen it repeated over and over again on LinkedIn, so it must be true right?

Read more “Cyber Myth: Attackers only have to be right once, Defenders have to be right all the time!” →
AI

When AI goes wrong…

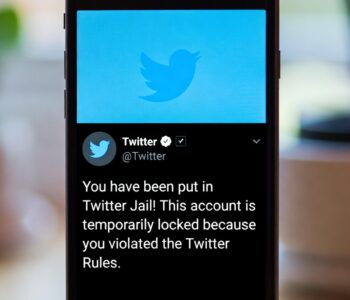
Ok so as I’m writing this I’m currently on a temporary ban from twitter…. the reasons for this I believe are more complex than one would expect. Full disclosure, I’m assuming the ban was in part due to AI but that is an assumption… but it’s the only realistic explanation I have. You might be thinking, who cares…. but bear with me….

Read more “When AI goes wrong…” →
AI

one step closer to Skynet?

Yesterday I ran a pentest against an RDP server, the process was ok but not amazing, I had to provide more help than I would have liked, resource consumption and the idea it should keep going…. wasn’t great. The process and output wasn’t terrible at all but it didn’t blow me away.

So today I wanted to see if Claude could take on as simple active directory lab! Now let’s be clear, there were I think one or two updates to the Claude client in that time! The Claude UI even changed look and feel! So I span up an AD lab I had made a while ago and got to work!

Read more “one step closer to Skynet?” →
Threat Intel

FortiSIEM CVE-2025-64155 Exploitation Analysis

‘An improper neutralization of special elements used in an OS command (‘OS Command Injection’) vulnerability [CWE-78] in FortiSIEM may allow an unauthenticated attacker to execute unauthorized code or commands via crafted TCP requests.’

https://www.fortiguard.com/psirt/FG-IR-25-772

This analysis was conducted using data from Defused, enrichment from IPINFO and SHODAN and then analysis using an LLM (GROK) (so take the analysis with a pinch of salt):

Read more “FortiSIEM CVE-2025-64155 Exploitation Analysis” →
Threat Intel

Fortiweb – CVE-2025-58034

‘CVE-2025-58034 is an OS command injection vulnerability (CWE-78) in Fortinet FortiWeb, allowing an authenticated attacker to execute unauthorized code on the system through crafted HTTP requests or CLI commands. It affects versions including FortiWeb 8.0.0-8.0.1, 7.6.0-7.6.5, 7.4.0-7.4.10, 7.2.0-7.2.11, and 7.0.0-7.0.11. The vulnerability has a CVSSv3 score of 6.7 (medium severity) and has been observed exploited in the wild, prompting its addition to CISA’s Known Exploited Vulnerabilities catalog.’

Read more “Fortiweb – CVE-2025-58034” →