 Vulnerabilities
I like to MoveIT MoveIT
Fast publish: If the past gives us any indication for the future, if you are running MoveIT you want to be aware of:
Read more “I like to MoveIT MoveIT”
Vulnerabilities
Fast publish: If the past gives us any indication for the future, if you are running MoveIT you want to be aware of:
Read more “I like to MoveIT MoveIT” Threat Intel
Mass iternet exploitation events are never fun, this week we have CVE-2026-41940 being exploited! Luckily we have the awesome and cool honeypots at Defused to help us investigate threat actor activity! So let’s take a look! (there’s a good writeup here from Watchtowr.
We have used ‘AI’ (Claude) to create a timeline based on packets from Defused honeypots:
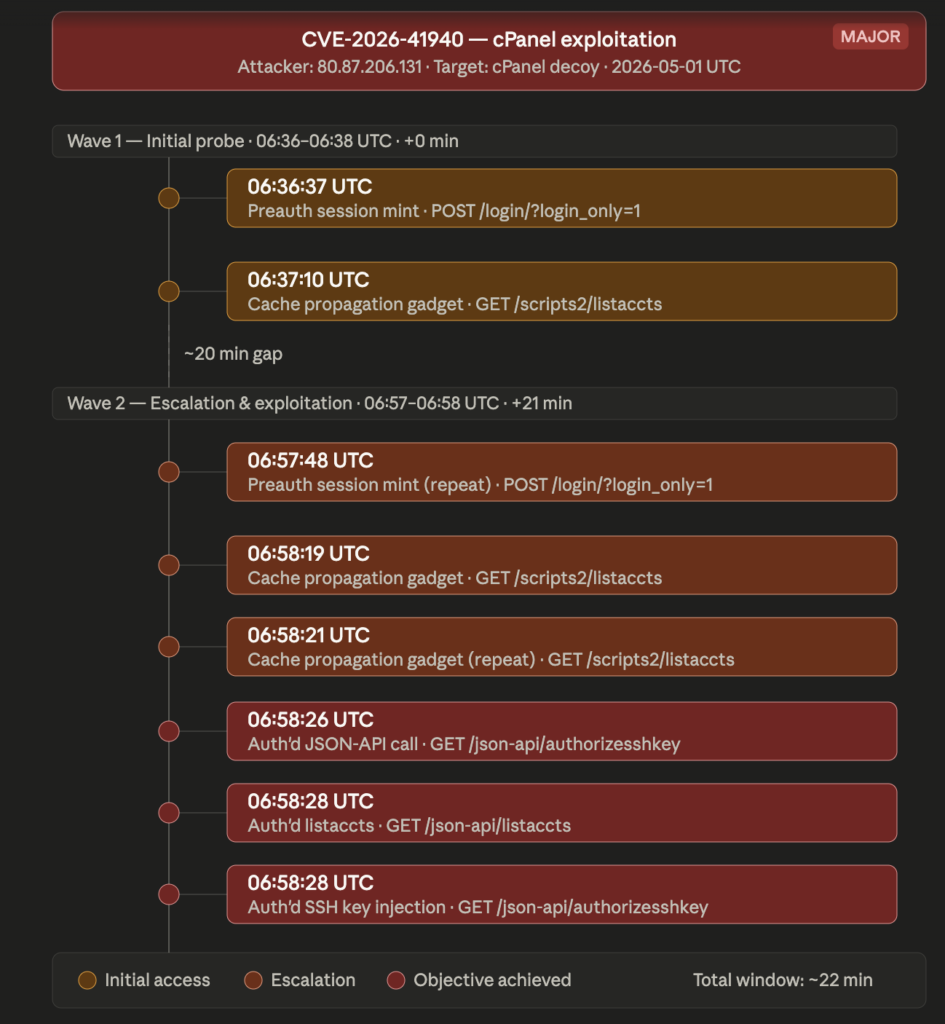
I exported the logs from the Defused honeypot TI feed focused on a single IP then imported that include a chat with Claude:
Here’s the breakdown of what the data shows:
Attack summary — CVE-2026-41940 against a cPanel honeypot
The attacker at 80.87.206.131 ran a structured, two-wave exploitation chain over approximately 22 minutes. The CVE pattern maps to a known cPanel authentication bypass class: forge a session via the preauth endpoint, propagate it through a cache gadget, then leverage the resulting authenticated context to make privileged JSON-API calls.
Wave 1 (06:36–06:37) was a minimal two-step probe — session mint followed immediately by a single cache propagation attempt. This is consistent with tooling running an initial reachability check before committing to full exploitation.
Wave 2 (06:57–06:58) is the main effort. The attacker repeated the session mint, fired the cache gadget twice (likely confirming propagation), and within 9 seconds of the second gadget request had transitioned to authenticated API calls — specifically authorizesshkey (SSH key injection) and listaccts (account enumeration). The two events timestamped 06:58:28suggest either a scripted burst or the tooling executing the auth’d phase in parallel.
Key indicators for hunting:
POST /login/?login_only=1 as the session mint vectorGET /scripts2/listaccts as the cache gadget trigger/json-api/ endpoints within seconds of gadget confirmationWorth checking whether 80.87.206.131 appears in any other decoy logs — the structured cadence strongly suggests an automated exploit kit rather than manual operation.
We can see here, the exploit here is very simple, POST then a GET followed by API access!
Not only do we now have data to write detections from, we can also look at creating a PoC for penetration testing and vulnerability assessment purposes! A double win! This really goes to show how valuable honeypots can be from a broad TI perspective as well as supporting defence and offence!
A double edged sword (or pot?), like so many things in life!
Each scenario is different so I’ll not try and tell everyone exactly what they should do here, the key point of this blog is to highlight the vulnerability, the threat/risk so people can take the appropriate steps.
Also, you probably want to check out the honeypots at Defused! They are awesome!
[update] just found this in the packets: H2ckt3ch@g0dl1k3 (cm9vdDpIMmNrdDNjaEBnMGRsMWsz is the BASE64). I won’t publish all the packets right now (because that probably won’t help this early on) but this string was interesting…
 Education
The future is here today! Ok, perhaps that’s a bit over dramatic, however there’s one thing in cyber security that is and has always been a general problem: Passwords! So enter the lord and saviour of all cyber security: Passkeys! (ok, they aren’t but they are cool and useful in a range of scenarios!) Let’s take a deeper look.
Read more “Passkeys are better than passwords!” AI
Do you ever struggle to keep up with the cyber world? Not everyone is plugged into the internet 24/7 as some people (I swear I get offline sometimes!) so keeping up to date with the cyber world can be pretty tricky! Also who has time to read everything? no one that’s who! But what about if we used an LLM to read things for us and then give us an update? Well here’s an example of this!
Read more “Using AI in a positive (non scary) way” AI
Yesterday I ran a pentest against an RDP server, the process was ok but not amazing, I had to provide more help than I would have liked, resource consumption and the idea it should keep going…. wasn’t great. The process and output wasn’t terrible at all but it didn’t blow me away.
So today I wanted to see if Claude could take on as simple active directory lab! Now let’s be clear, there were I think one or two updates to the Claude client in that time! The Claude UI even changed look and feel! So I span up an AD lab I had made a while ago and got to work!
 AI
AI hype is everywhere, and don’t get me wrong, I’m a heavy AI user, I’m creating tools, conducting analysis and using AI constantly these days in my work a research. But I wanted to see, how well does an agent work if we try and give it the whole task to conduct with as minimal help as possible.
Read more “AI as the penetration tester” Threat Intel
This week there’s been a lot of activity on reporting on a compromise which occurred in 2025 in Poland.
I’m neck deep inside some project work so I don’t have time to pour over this but I did spent a few minutes prompting GROK.
“On December 29, 2025, Poland experienced a coordinated and destructive cyber attack targeting its electric grid, specifically focusing on distributed energy resources (DERs) such as more than 30 wind farms, solar (photovoltaic) installations, and one major combined heat and power (CHP) plant that supplies heat to nearly half a million residents. The assault, which occurred amid harsh winter weather including low temperatures and snowstorms, exploited vulnerabilities like exposed FortiGate firewalls/VPNs lacking multi-factor authentication, default or weak credentials on devices (e.g., Hitachi RTUs, Mikronika controllers), and poor network segmentation. Attackers gained access to operational technology (OT) systems, deploying wiper malware (including variants like DynoWiper and LazyWiper), overwriting disks, deleting files, resetting configurations, and uploading corrupted firmware to “brick” certain hardware—resulting in permanent field-level impairment and complete loss of remote monitoring and control at affected sites. Despite these actions, no power outages or heat supply disruptions occurred, thanks to the grid’s coal-heavy inertia, resilient generation continuity, and partial mitigations such as endpoint detection and response (EDR) blocking wipers in the CHP environment.
 Threat Intel
Imagine this, you setup a server and it has a really weak administrator password! Now let’s imagine you expose RDP to the internet. How long would it take to get pw3nd?
Well we did this, using a custom configuration to make this safe, we setup a Windows Server, setup an administrator account with the password of ‘password’ and monitored the logs! So let’s see what we found.
Read more “Administrator:password” Threat Intel
‘An improper neutralization of special elements used in an OS command (‘OS Command Injection’) vulnerability [CWE-78] in FortiSIEM may allow an unauthenticated attacker to execute unauthorized code or commands via crafted TCP requests.’
https://www.fortiguard.com/psirt/FG-IR-25-772
This analysis was conducted using data from Defused, enrichment from IPINFO and SHODAN and then analysis using an LLM (GROK) (so take the analysis with a pinch of salt):
Read more “FortiSIEM CVE-2025-64155 Exploitation Analysis”
Education
Ad tech is a threat that really doesn’t get much airtime! So let’s do quick demo:
Read more “A tech demo – Gyroscope & Accelerometer Detector”