Leadership

How likely is successful mass exploitation of PHP2SHELL?

Never in a high alert scenario should be try and be too solid with our predictions, because this game is difficult! but given PHP2SHELL day is such a mad day, I’m going to break my typical model, however:

Personal view: this is a HIGH ALERT scenario but not an ACTIVE EXPLOITATION scenario (at the time of writing), so this is SERIOUS and requires paying attention to!

but the question, how likely is this to lead to mass exploitation? is there REAL tough and serious question we have to ask when considering the wider landscape of national security etc. so I’m going to at least explore it a bit!

Read more “How likely is successful mass exploitation of PHP2SHELL?” →
Leadership

Upgrading to PHP 8.5.12 Backports

Ok so, some fun notes:

Cloudflare deployed blocking rules at about 1500 today!

Ubuntu back ported the fixes so this server is now patched!

The world, so far hasn’t ended!

Pwndefend stayed online, whilst many others… did not! That speaks volumes for their defence in depth perhaps….

Let’s see where this PHP cyber journey will go!

AI

Machine Speed

I have been both watching/listening and in meetings where I have heard some ‘interesting’ statements about ‘machine speed’ hacking by with unlimited capacity and unlimited speed….

You can, if you know me, imagine my expression on my face, however I figured let’s not settle for ‘Trust me bro it doesn’t work like that’, let’s do some SCIENCE!

(I know everyone loves scientists these days after they pluck numbers out of their ass and say things like: there is a 10-70% chance AI will destroy humanity in the next 5 years’ (and have zero evidence for the math let alone evidence for the risk model other than ‘trust me, I’m super smart’).

I’m not that smart so I do actual testing of theories, and then I share things, I know, I’d make a terrible ‘scientist’. It’s hot in the lab today so this will be a quite a brief view but should contain the key details.

Read more “Machine Speed” →
Strategy

From TimThumb to wp2shell: 25 Years of WordPress Mass…

TL;DR: wp2shell (CVE-2026-63030 chained with CVE-2026-60137) matters because it is a core, pre-authentication RCE reachable on a stock, plugin-free install. That is the rare category. In 25 years, unauthenticated code execution against a bare WordPress install has happened only a handful of times. The overwhelming majority of WordPress mass compromise has ridden the plugin and theme supply chain and infrastructure abuse, not core. This post maps the history so you can see where wp2shell actually sits.

Read more “From TimThumb to wp2shell: 25 Years of WordPress Mass Exploitation” →
Vulnerabilities

WP2SHELL Update

This morning I’ve started to see exploitation attempts on pwndefend.com (they all failed because like about 80% of sites (based on sampling) this site automatically patched, but also, this site has word fence, is fronted by Cloudflare.

Global Exposure

On the 18th (AM) I did sampling of about 3.5K hosts and found ~20% were not patched. The cyber apocalypse is not seemingly here today! (let alone the fact that if every WordPress site was popped, the world would probably not end)

Read more “WP2SHELL Update” →
Threat Intel

Bleeding Out

When you compromise a firewall you have lots of options in terms of next steps, from using the VPN, changing configurations, creating backdoors or perhaps using the firewall to PCAP. In this post I’m going to explore the ‘Fortibleed’ campaign. I have to note, we can see in honeypot logs this TA did not seem to limit themselves to Fortinet exploitation, however the area of analysis has a heavy Fortinet element. You will see they deployed a capture and analysis platform. Treat everything with a pinch of salt because I’m using a mad probability based machine (LLM) to support me for this!

Read more “Bleeding Out” →
AI

When AI goes wrong…

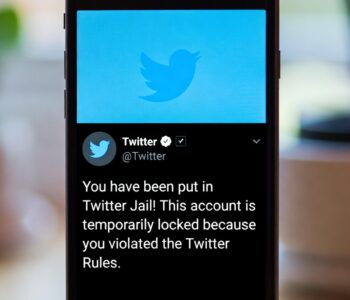
Ok so as I’m writing this I’m currently on a temporary ban from twitter…. the reasons for this I believe are more complex than one would expect. Full disclosure, I’m assuming the ban was in part due to AI but that is an assumption… but it’s the only realistic explanation I have. You might be thinking, who cares…. but bear with me….

Read more “When AI goes wrong…” →
Threat Intel

FortiSIEM CVE-2025-64155 Exploitation Analysis

‘An improper neutralization of special elements used in an OS command (‘OS Command Injection’) vulnerability [CWE-78] in FortiSIEM may allow an unauthenticated attacker to execute unauthorized code or commands via crafted TCP requests.’

https://www.fortiguard.com/psirt/FG-IR-25-772

This analysis was conducted using data from Defused, enrichment from IPINFO and SHODAN and then analysis using an LLM (GROK) (so take the analysis with a pinch of salt):

Read more “FortiSIEM CVE-2025-64155 Exploitation Analysis” →