Leadership

How likely is successful mass exploitation of PHP2SHELL?

Never in a high alert scenario should be try and be too solid with our predictions, because this game is difficult! but given PHP2SHELL day is such a mad day, I’m going to break my typical model, however:

Personal view: this is a HIGH ALERT scenario but not an ACTIVE EXPLOITATION scenario (at the time of writing), so this is SERIOUS and requires paying attention to!

but the question, how likely is this to lead to mass exploitation? is there REAL tough and serious question we have to ask when considering the wider landscape of national security etc. so I’m going to at least explore it a bit!

Read more “How likely is successful mass exploitation of PHP2SHELL?” →
AI

Machine Speed

I have been both watching/listening and in meetings where I have heard some ‘interesting’ statements about ‘machine speed’ hacking by with unlimited capacity and unlimited speed….

You can, if you know me, imagine my expression on my face, however I figured let’s not settle for ‘Trust me bro it doesn’t work like that’, let’s do some SCIENCE!

(I know everyone loves scientists these days after they pluck numbers out of their ass and say things like: there is a 10-70% chance AI will destroy humanity in the next 5 years’ (and have zero evidence for the math let alone evidence for the risk model other than ‘trust me, I’m super smart’).

I’m not that smart so I do actual testing of theories, and then I share things, I know, I’d make a terrible ‘scientist’. It’s hot in the lab today so this will be a quite a brief view but should contain the key details.

Read more “Machine Speed” →
AI

Getting less wrong about computing

The last two weeks online have been like a flood, I’m not even sure what words to use to describe them accurately, but I’ll give this a go:

  • Disinformation
  • Misinformation
  • Hype

I have been shocked really at what has occurred, in front of me:

  • Mass hysteria
  • Media hosting people constantly who are making unprovable claims with seemingly no real challenge

It’s been frankly exhausting to watch, let alone being involved in a range of discussions online:

  • I’ve seen people actually say things like: we have created a new lifeform, AI is alive etc. (paraphrasing)
  • I’ve had people tell me that these computing systems are not computers (WTF)
  • I’ve seen journalists essentially platform and parroting people with what appears to be significant loss of grasp of science and reality.

So I’ve been quite active online (whilst trying to field off questions from friends, family and colleagues about: is AI going to kill us? (good god how much time has been wasted!) but also I’ve been trying to give people a view of reality TODAY! So that’s partly what this blog is about!

Read more “Getting less wrong about computing” →
Threat Intel

WP2SHELL

Yesterday afternoon/early evening a patch for WordPress was released (7.0.2) which address two vulnerabilities which are named: WP2SHELL. This is a fast post (largely generated by Claude Opus) to provide some detail. For reference in our research we have found ~20% of WordPress sites still vulnerable as of a few hours ago (based on a sample), so this is a live scenario and it would be strongly advisable for organisations to take appropriate steps. This morning I’ve built a docker lab of a vulnerable WordPress site and demonstrated hash theft and web shell deployment to a vulnerable lab instance.

I’ve put some resources for people (use at own risk) into a repo: https://github.com/mr-r3b00t/wp2shell/

that includes a scanner, some info on the vulns and a PoC tool!

Read more “WP2SHELL” →
AI

AI: Fear it, so I can sell you the…

We are already watching the fear, uncertainty and doubt industry spin up around AI. It follows a pattern anyone who has sat through a vendor pitch will recognise: take a real, narrow signal, strip out the caveats, and inflate it until it fills a keynote slide or a board paper. The problem is not that AI carries no risk. It carries plenty. The problem is that the loudest claims are almost always the least accurate, and the people making them usually have something to sell — a model, a defence against one, or a regulatory moat.

So let’s take the three narratives I keep hearing, put them next to the evidence, and separate the kernel of truth from the theatre.

Read more “AI: Fear it, so I can sell you the cure!” →
Leadership

Email Security: An Enablement Journey, Not a Maturity Ladder

Most organizations treat email authentication as a checkbox exercise. Deploy SPF, publish DMARC in reporting mode, call it done. But the real story isn’t about maturity tiers—it’s about what you unlock at each phase of implementation. And frankly, the gap between where organizations are and where they need to be is brutal.

This post outlines an enablement journey: each phase builds on the previous one and creates new capabilities that weren’t possible before.

Read more “Email Security: An Enablement Journey, Not a Maturity Ladder” →
Cybercrime

Using shame to enable extortion

When we look at ‘sextortion’ and ’email based extortion’ tactics used by threat actors we see a common pattern, one that leverages shame & fear. I’ve worked with some victims of this and it’s really not nice for them, the impacts are not just financial, they are emotional and sometimes more. It’s fortunately (for me) don’t however deal with this in volume, however I wanted to highlight something, the similarities between extortion and what I would describe as ‘Security Scanning’ shame scamming. Now you might think, that’s a massive leap… but bear with me, I’ve been looking at this (CTI/OSINT) plus working with ‘victims’ for years…

I’ll be posting about some research I’ve done on DNSSEC shortly too, I’ve kind of figured this topic was over years ago, but it’s recently come back on my radar, you know sometimes ‘duty calls’. But let’s look at shame based extortion patterns for now:

Read more “Using shame to enable extortion” →
Threat Intel

cPanel Vulnerability Exploited ITW

Mass iternet exploitation events are never fun, this week we have CVE-2026-41940 being exploited! Luckily we have the awesome and cool honeypots at Defused to help us investigate threat actor activity! So let’s take a look! (there’s a good writeup here from Watchtowr.

Kill Chain

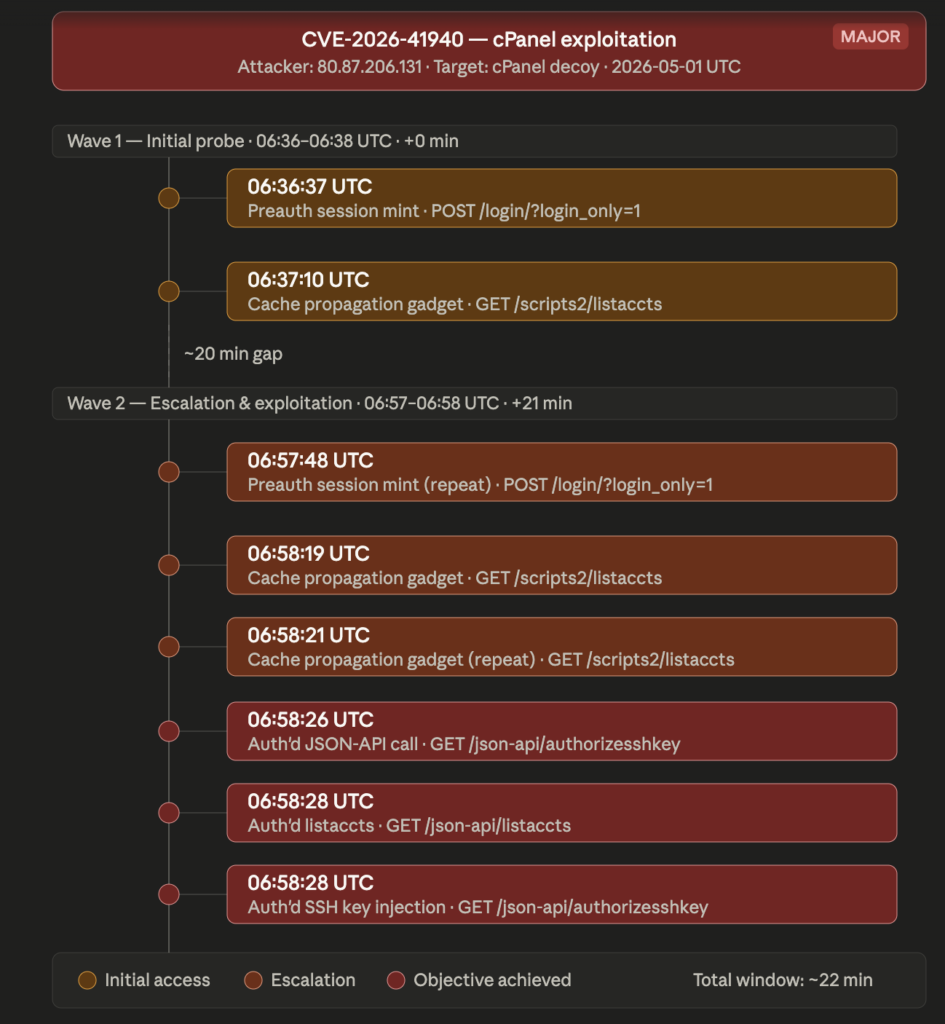
We have used ‘AI’ (Claude) to create a timeline based on packets from Defused honeypots:

What did Claude say?

I exported the logs from the Defused honeypot TI feed focused on a single IP then imported that include a chat with Claude:


Here’s the breakdown of what the data shows:

Attack summary — CVE-2026-41940 against a cPanel honeypot

The attacker at 80.87.206.131 ran a structured, two-wave exploitation chain over approximately 22 minutes. The CVE pattern maps to a known cPanel authentication bypass class: forge a session via the preauth endpoint, propagate it through a cache gadget, then leverage the resulting authenticated context to make privileged JSON-API calls.

Wave 1 (06:36–06:37) was a minimal two-step probe — session mint followed immediately by a single cache propagation attempt. This is consistent with tooling running an initial reachability check before committing to full exploitation.

Wave 2 (06:57–06:58) is the main effort. The attacker repeated the session mint, fired the cache gadget twice (likely confirming propagation), and within 9 seconds of the second gadget request had transitioned to authenticated API calls — specifically authorizesshkey (SSH key injection) and listaccts (account enumeration). The two events timestamped 06:58:28suggest either a scripted burst or the tooling executing the auth’d phase in parallel.

Key indicators for hunting:

  • POST /login/?login_only=1 as the session mint vector
  • GET /scripts2/listaccts as the cache gadget trigger
  • Rapid pivot to /json-api/ endpoints within seconds of gadget confirmation
  • 20-minute gap between waves is characteristic of automated tooling with a callback/retry loop

Worth checking whether 80.87.206.131 appears in any other decoy logs — the structured cadence strongly suggests an automated exploit kit rather than manual operation.


We can see here, the exploit here is very simple, POST then a GET followed by API access!

Not only do we now have data to write detections from, we can also look at creating a PoC for penetration testing and vulnerability assessment purposes! A double win! This really goes to show how valuable honeypots can be from a broad TI perspective as well as supporting defence and offence!

A double edged sword (or pot?), like so many things in life!

Suggested Actions to take

  • Check if you or your hosting providers run CPANEL
  • Check for compromise (or request intel from a partner)
  • If no compromise detected patch the server
    • if you can’t patch consider using an IP allow list/VPN or other method to shield access from anywhere on the internet (you might want to do this even if you have patched)
  • If compromised follow your incident repsonse process

Each scenario is different so I’ll not try and tell everyone exactly what they should do here, the key point of this blog is to highlight the vulnerability, the threat/risk so people can take the appropriate steps.

Also, you probably want to check out the honeypots at Defused! They are awesome!

[update] just found this in the packets: H2ckt3ch@g0dl1k3 (cm9vdDpIMmNrdDNjaEBnMGRsMWsz is the BASE64). I won’t publish all the packets right now (because that probably won’t help this early on) but this string was interesting…