 Threat Intel
Another day, another vulnerability, as has been so… for basically forever. However if you run PHP you don’t want to sleep on this one, due to some shenanigans there’s been an ‘early release of intel’ (leak) and a patch for PHP is on the way, however there’s also now a PoC in the wild! But the devil, as always is in the details! So let’s explore those, as always this is a fast publish and you should look to the vendor for guidance etc. with that important caveat aside, let’s explore:
The quick intel
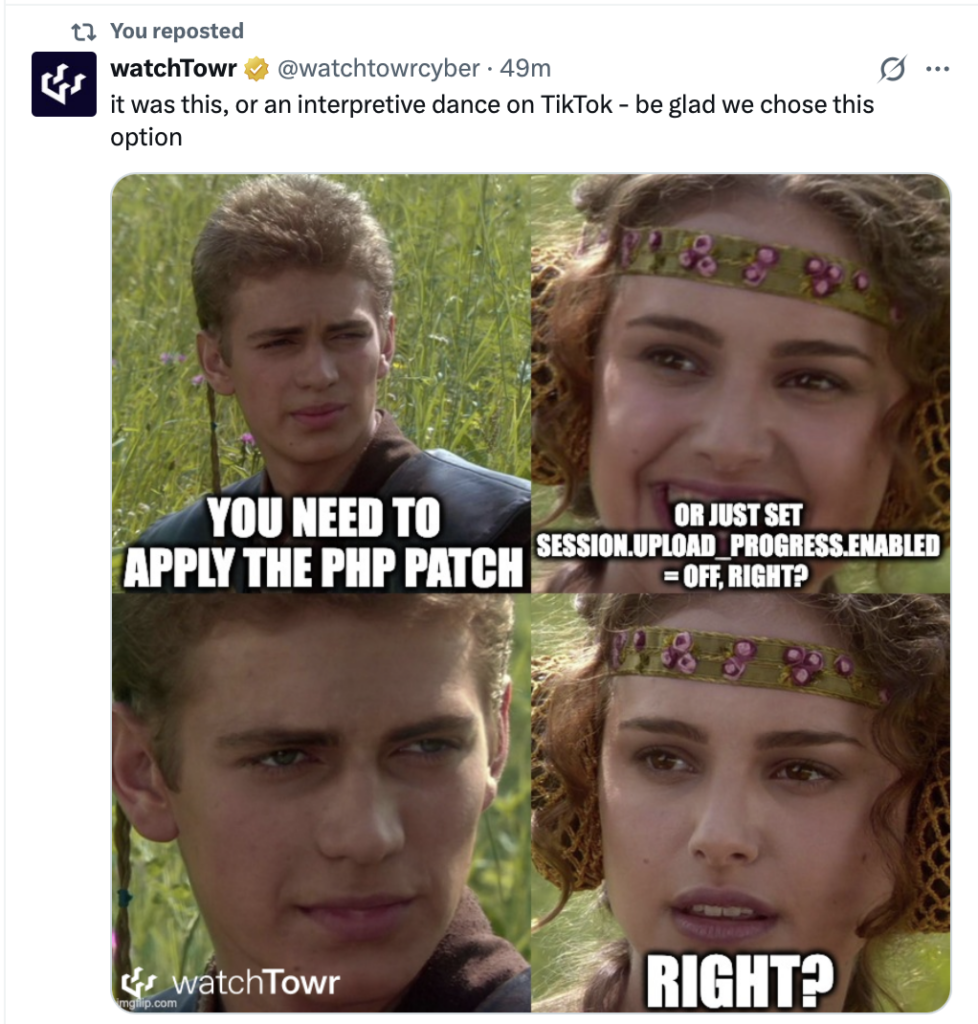
There was lots of guidance saying to change a PHP config, according to WatchTowr this does not work.
The vulnerabilities
First I used the power of my eyeballs and brain to read the two POC scripts (python), always sensible to use ones brain! Then because time, I then parsed these through claude with OPUS 4.8 to produce a report on these!
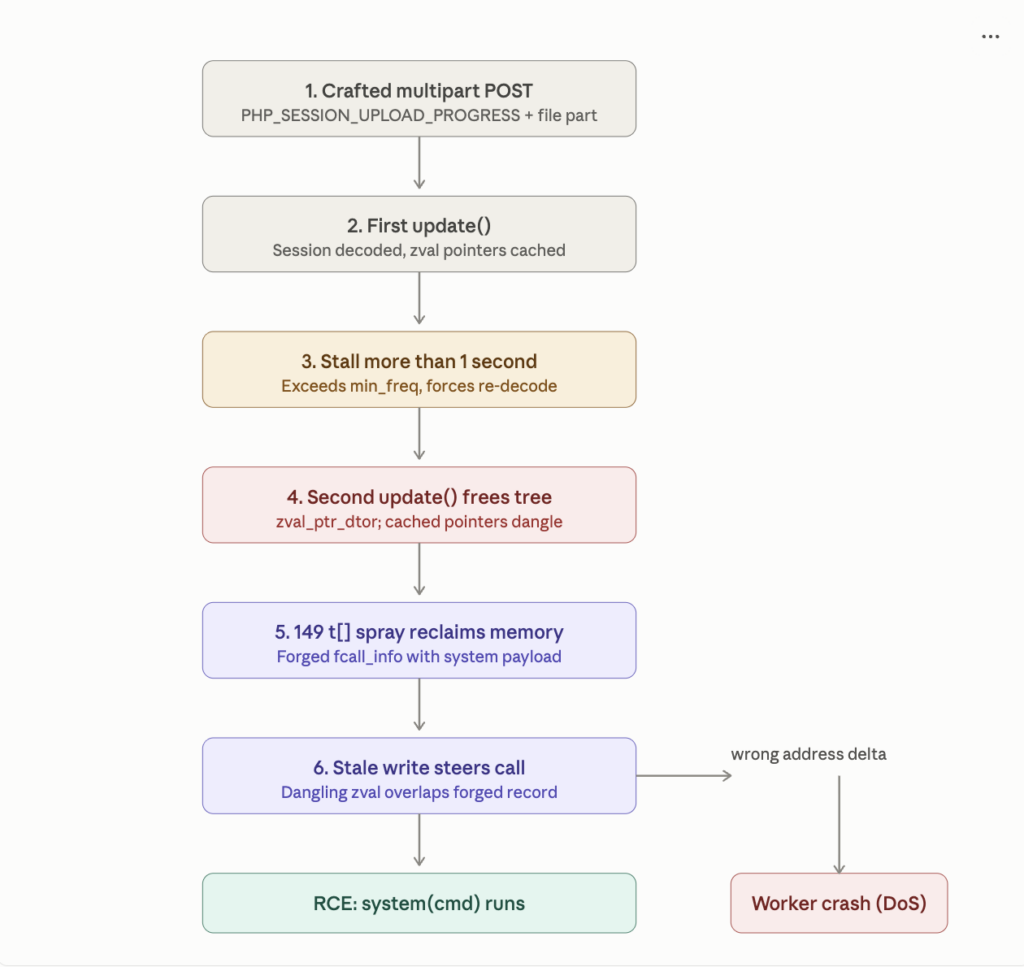
We can see here that we have likely DoS conditions with a chance of RCE.
Update: the first POC was ‘a bit janky’ – more to follow later! – the fluid world of cyberz!
Some more key findings:
Not only will this brute force and possible cause DoS (so it’s noisy!) the payload also has to be keyed for each PHP version.
I’ve just tested the POC at ‘the wrong version’ of PHP in the LAB (PHP 8.3.6) and we didn’t experience DOS. I’m still running tests so more to follow:
As always check with your vendors: https://www.php.net/archive/2026.php#2026-10-20-1
For up to the minute explorations/research as always see me on Twitter! https://x.com/UK_Daniel_Card
Update: 21/10/2026 11:02 UTC – It appears the PoC is non functional against actual targets:
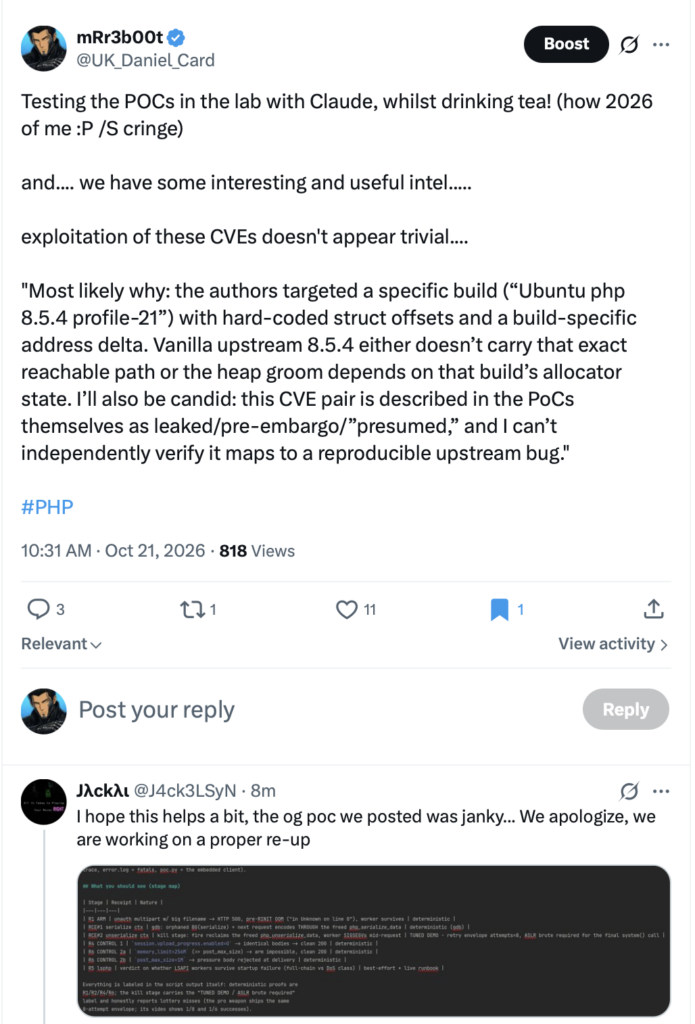
Update 21/10/2026 11:38: Guidance from UK NCSC added:
https://www.ncsc.gov.uk/news/critical-security-issue-affecting-php
Update: New POC available and is running in the lab….
Update: MEMES from watchtowr suggest the config change is NOT enough:
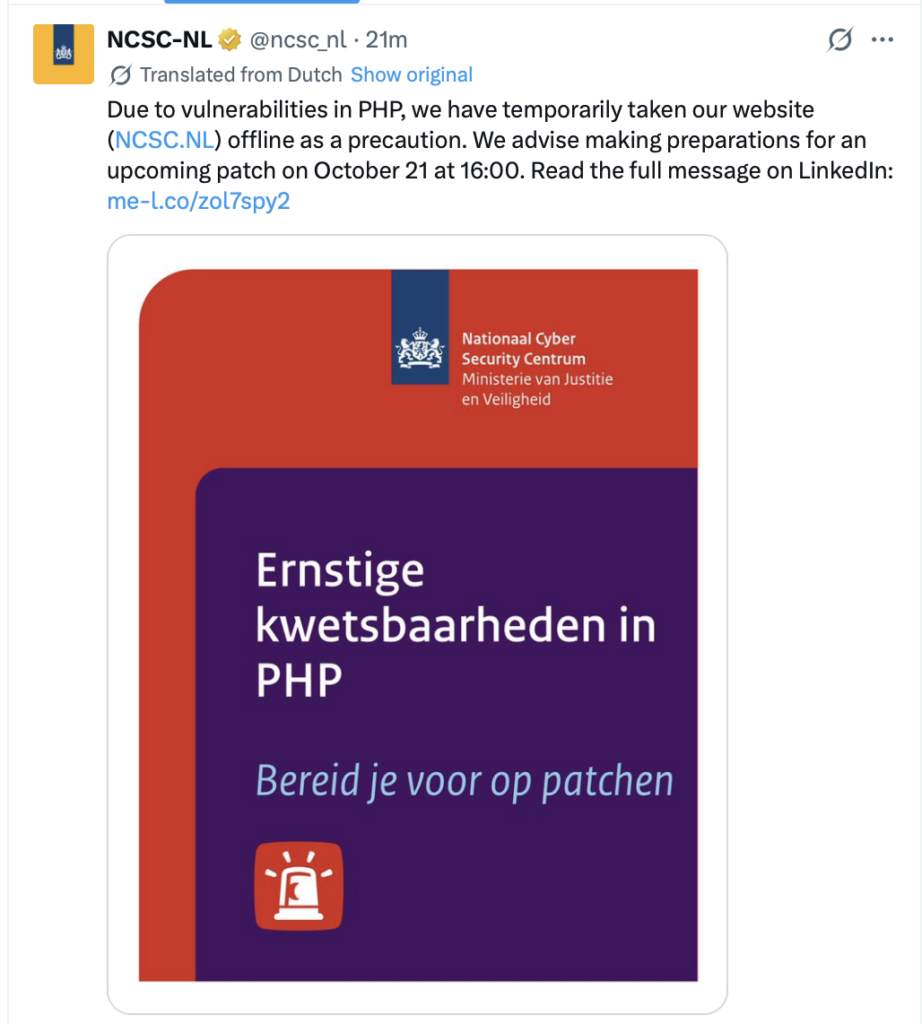
Update: 12:36 NCSC Netherlands has just pulled their website:
Update 12:44: I’ve just reproduced DoS in the LAB against a server running PHP….