 Leadership
2026… the era of… hacking
I say this tongue in cheek, it’s 2026 and the world is experiencing a range of ‘interesting’ times, I’m not going to pass judgment hear but I am going to show some things form the real world that I’ve observed. They are AI (LLM) related!
A key challenge when organizations deploy ‘new’ technology solutions is that often they deploy first, think about security later. I believe I would not be too out of turn too suggest that’s been repeated over the lsat 30 years with computing and once again with AI, society is doing the same thing, again… who could have guessed! /S
AI Risk Scenarios
Whilst the media is filled with “Threat Actors with AI can cyber attack you at M*chine Speed with Unlimited Scale…* (god please make it stop), there are obviously risk scenario of external threat actors using LLMs, however, there’s far more than that!
- Internal users using LLMs and them being prompt injected or ‘hallucinating’
- Internal users abusing LLM tools for malicious purposes
- Internal users using an LLM and the produced output is malicious ‘by accident’
- Eternal competitors pulling apart your products and hacking you
- Public facing chatbots are abused by external threat actors
- Internal systems are comprised and external threat actors use your own LLMs against you
This is not all the possible scenarios, but it’s some that are real and some that you might not have considered that have, in fact materialized!
Scenario 4 would sound unlikely however the internet may have shown, perhaps the likelihood of that is higher?
Scenario 3, you probably would assume this could not occur right… but I promise you, that’s also not impossible either!
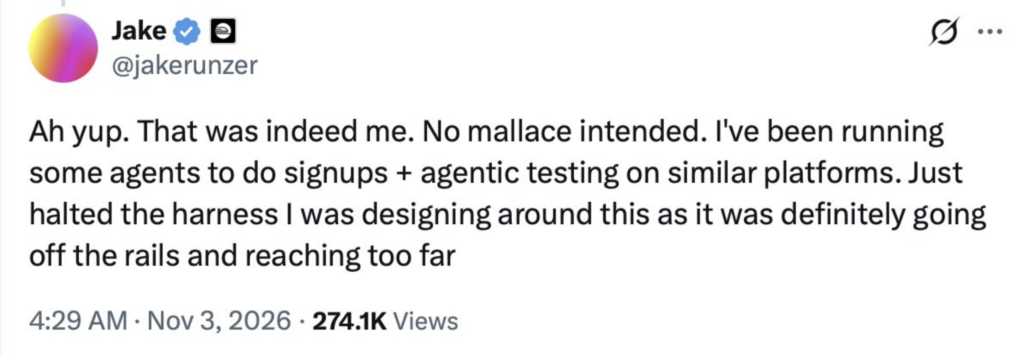
It’s been a long long few weeks (and still we haven’t been wiped out by a CVE, who knew /s!), so I’m going to keep this one short. Remember, risk assessments before you deploy are useful easier than post deployment, change things once they are in motion is difficult!
- Ensure you do actually do risk assessments before you deploy!
- Ensure you have AUPs in place for AI usage
- Ensure you are very careful with what you allow code to do on your endpoints/devices
- Consider as well LLM integrated systems (especially public facing chatbots)
- Take an adversarial approach to thinking
- Assume breach mindsets really are useful
- Monitoring is important, with LLMs it’s like having to monitor a custom LOB app but that app is on every endpoint, in every web server and there’s third party ones….. a minefield!
oh and just because someone claims they hacked something (the fridges for example) it doesn’t mean they did! even if they do have ‘AI’!