 Leadership
Restrict Access to Management Interfaces
Can you remember when you first heard about this? I’m 43 as I write this, and I’ve been working for over 26 years, and I wouldn’t be able to tell you when. The ‘age of the internet’ has been a long journey.
I was first online at home in the 1990s, I remember playing games over dial up between friends by modem, then moving online to play games like Quake over TCP/IP. The first ping level I had during a game was over 1000 milliseconds! (Basically at that latency I died lots and didn’t really play but…. I was online with other people fighting each other! so cool!). But what has our security journey looked like? Let’s take a walk through this but more from a my eyes perspective, than just a history timeline, I think that might be more interesting!
Peering back in time
I’m going to mix this journey with some key moments I can remember and then possibly some historic incidents, my memory is terrible so I’ll be using an LLM/the internet to help me as I go:
My first PC was an amstrad, I’m not even going to try and think about the model, but that was 100% not online. The first intel x86 PC I had was a 486 DX 66Hmz, which was an upgrade from my mother’s 386! So I was rocking some speeds! Who remembers the TURBO button!? Ah good times, and really this was probably the start of my career journey, the home PC! Apparently it was for the family, but let’s be real, no one else could get a looking! This is from an age where we had Encarta on CD-ROM!
I think our first internet connection came from PIPEX (founded in 1990), and It would have been around 1994/95 when I first got online. Hell at one point we had AOL etc.
Let’s think about the device we had, a 486, running Windows 3.11 and DOS 6.2. What did our security look like?
Well we had a modem, our PC was bare back to the internet via MODEM, Windows 3.11 didn’t have a built in firewall, no antivirus… I would have been using ICQ etc.
So I think we can say reasonably so that there was a very weak security posture! In 1995 I would have upgraded Windows 3.11 to Windows 95! I upgraded to 98, in well 98! It was a simpler time back then, we could use OS names to know how modern something was!
This must have been around the times of WINNUKE and PING OF DEATH….. you see my memory will struggle here loads. The period of 3.11 to Windows 2000 and beyond, well I started doing things to troubleshoot computers when I was a kid (I helped in some orgs via family), and the first real malware incident I had was with the FORM virus, a printing company had their machines infected (Mum worked there) and we had the job of doing IR! Floppy disk based incident response, ha, that was ‘fun’ (I mean I did actually have fun!)
My first work experience was working in the IT department of a travel company, so we supported:
- NT 4 Server (and terminal servers/Metaframe Servers)
- Windows 95
- Windows 96
- Windows 3.11
- NT4 PRO
- MS Proxy Server 2.0
- Exchange 5.5
- and a bunch of other stuff, CISO firewalls, I can’t remember what switches! (it was a long time ago now!)
I was allowed to install the first Windows 2000 server in a test environment, omg that was so fun! I learned here that cage nuts are also the IT persons eternal enemy! Sharper than any sword! lethal! This was a time when digital security was frankly terrible, sure we had NT4 domains, with PDCs and BDCs etc. But mostly if you got physical access to a computer you could use press cancel at the logon screen and get access to data and have ‘admin rights’ locally.
With NT4 that could be different, but largely we had NT4 Domains and Windows 95/95 clients, and software aside you could just open the case and plug the hard disk into another PC and read all the data! Full disk encryption as standard would come far later, and hell, we did not even have host based firewalls really! This was truly a very different world to what we have today!
Blasting into the future
Host based firewalls would not come around in force until 2003, post MSBLASTER! At this point in time, it was now known to restrict management interfaces, but really that wasn’t done often in practise, that as is now really depends on how something has been deployed and configured, however if we look into the history books we will find guidance like this: ‘Router Security Guidance Activity of the System and Network Attack Center (SNAC)’ from the National Security Agency (NSA):
How cool is this! https://www.cisco.com/E-Learning/bulk/public/celc/CRS/media/targets/resources_mod07/7_3_4_2RSCG.pdf
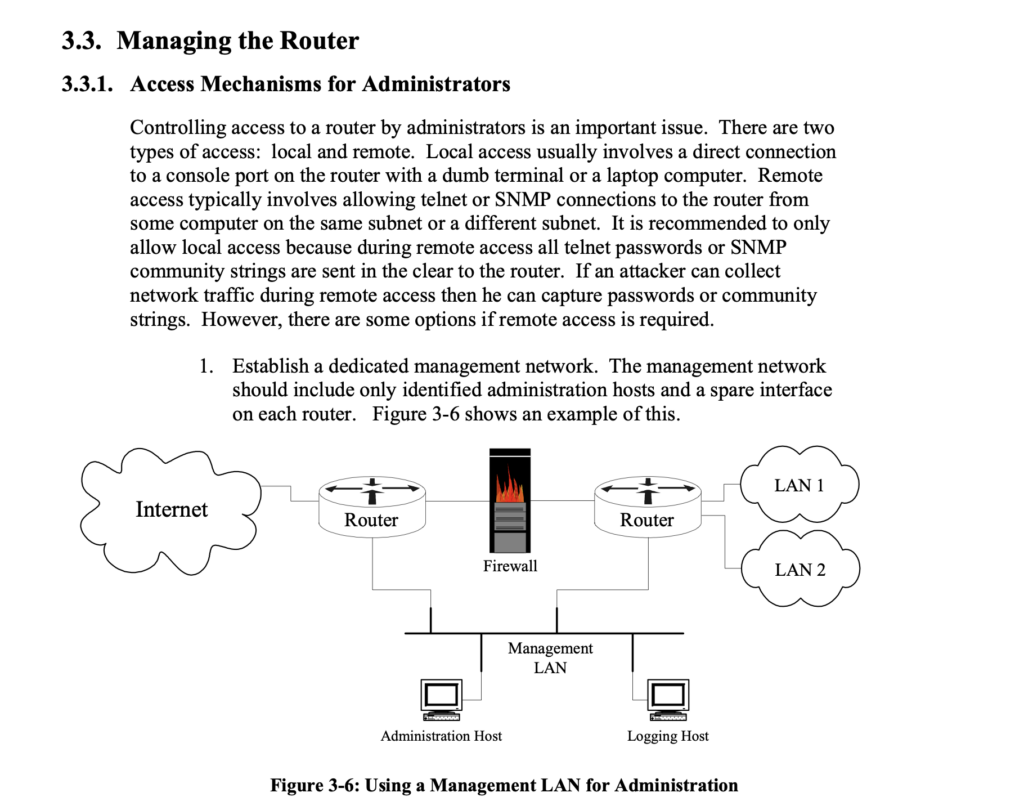
and look management LAN, and logging Hosts! I often say that with firewalls they should never have been sold without a logging/monitoring server!
So in this period of time I was working in gov networks and we were hit with MSBLASTER, this was a major incident, at least 50% of the systems were being blue screened constantly, the network was flat and well there’s a tale for another day but young r3b00t went to work, under cover from my colleagues who protected me from desktop support duties, I went to work on building counter scripts/tools to scan, enumerate, identify, evict and patch all the systems! This was basically my ‘counter worm’. We have to also remember the NACHI worm here as well! (Nachi caused DoS… it deffo wasn’t an authorised execution)
At this point we often needed serial cables to configure some network equipment, but also telnet was widely used and web interfaces for management were a thing! I think my firs CISCO firewall was a PIX, but back then, I was doing a lot of my networking on RRAS services on Windows. Flat networks were very much the norm! (and still largely are!).
So back in 2002 as an industry we knew we had to protect management interfaces and log/monitor… we didn’t really have host based firewalls on (by default) and full disk encryption by default wasn’t a thing, we probably only just around then had windows defender out of the box…. (there was internet connection firewall but it was not enabled by default).
What I’m going to show here, is not that we have (as society) got GOOD at cyber security, but we have perhaps got better….
Ok I’m calling in some clanker support, I need to get to do some work work but here, a timeline of changes over the years from a Windows client perspective:
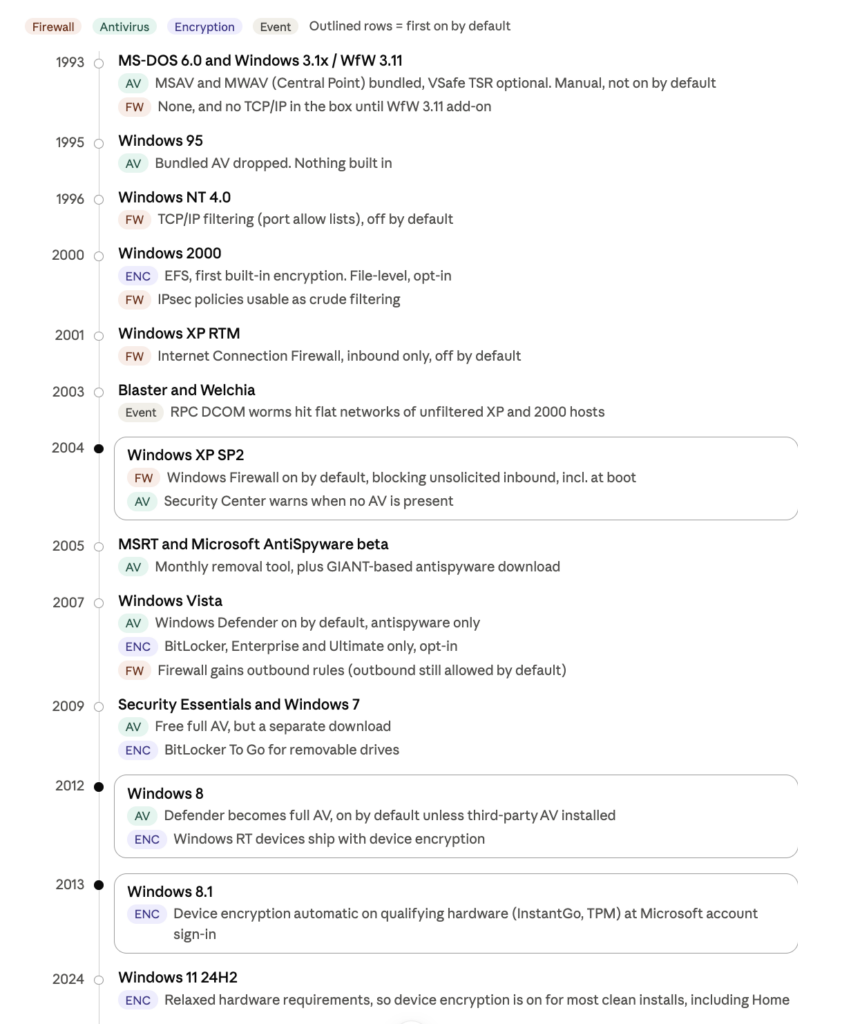
So, have we go better at cyber?
It’s an open question, the world is constantly changing and evolving and we have far more digital systems today than we used to, however, I for one know that today we have far better tools and capabilities to defend out systems than we ever had, if we choose to use them well, that’s another matter!
As someone who has lived their professional life through the timeline above, I believe the trend is, we are getting better, and I am hopefully for the future!! What do you think?