Defense

Why are ransomware attacks so devastating? – Part 1

Introduction

“Ransomware is a major issue!”

Hang on maybe we need to re-phrase that:

“Weak security postures are a major issue!”

or perhaps.. why not both!

I’ve been working with digital technology management for over 20 years, I started out when I was a kid (literally) fixing people’s PCs in their offices, removing malware, improving configurations, writing batch file menus, and playing games. As time has gone on technology has shrunk and continually become more and more of our everyday lives.

Back in 2003 I responded internally to MSBlaster, an SMB worm that had a devastating effect for the time, by today’s standards it was child play, however I remember saying “it’s a good job it didn’t delete everything whilst it was here.” (Or something very similar. Post NACHI/Blaster my friends and I were talking about how worse it could get. Fast forward in time and it’s much worse. Yet when I look at networks, they don’t look very different to how they did back in the 2000s.

Despite a multi-billion-dollar cyber security industry, it seems daily that organisations are succumbing to “cyber-attacks” which commonly include ransomware. Why are they successful and why are they so impactful? Well, let’s take a look! Read more “Why are ransomware attacks so devastating? – Part 1” →
Defense

Audit NTDS.DIT using DSINTERNALS

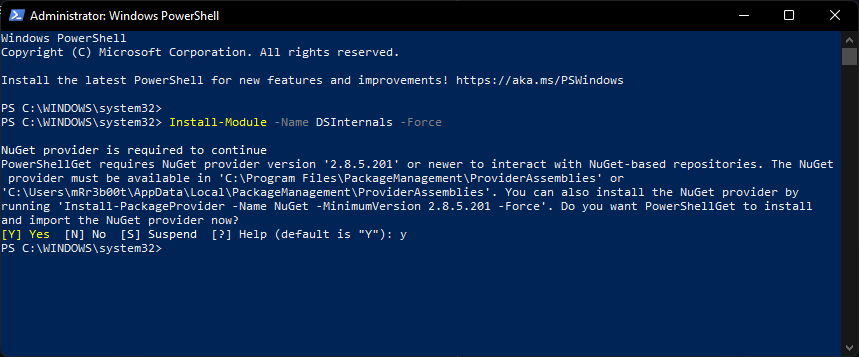
Ok this assumes you know how to get the NTDS.DIT and SYSTEM registry hive out from a domain controller, if you don’t go looking, we might have blogged a few ways to do that! Now then, firstly, let’s Install DSInternals. From PowerShell 5 onwards you can simply run:

Install-Module -Name DSInternals -Force

Text

Description automatically generated

You will likely need to set your execution policy:

Set-ExecutionPolicy -ExecutionPolicy Unrestricted

Now to dump the hashes we use: Read more “Audit NTDS.DIT using DSINTERNALS” →

Defense

Dumping Credentails with MIMIKATZ and Passing the Hash (PTH)

I kid you not, I forget the commands, so I thought, hey let’s write a small blog post on credential dumping and pass the hash.

To achieve this we need: Debug privileges on a single machine or we need access to a disk that does not have full disk encryption. We also need the password to be re-used.

Mimikatz

Ok for this demo I’m going to run with the out of the box release for Mimikatz on a domain joined windows PC with Defender disabled.

To gain system we launch mimikatz from an admin shell and run:

privilege::debug

token::elevate

Now we are SYSTEM we access a range of high privilege level areas. Read more “Dumping Credentails with MIMIKATZ and Passing the Hash (PTH)” →

Defense

Hacking Guide – AESREPRoast and Kerberoasting

Kerberos Pre-Authentication Hash Retrieval and Cracking

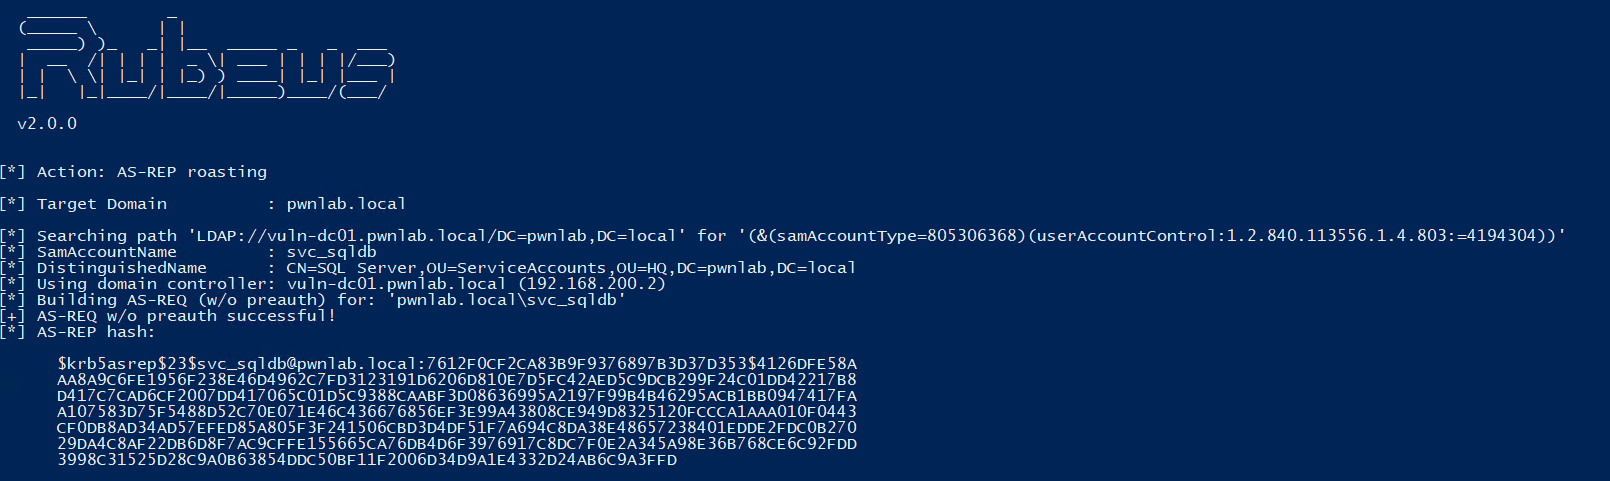
We can enumerate active directory to find accounts that do not require pre-authentication. There’s a simple way of doing this using Rubeus:

.\Rubeus.exe asreproast /format:hashcat

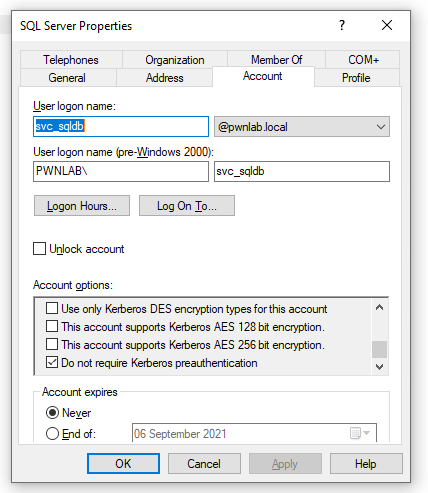
We can see there is a vulnerable account that has Kerberos Pre-Authentication disabled.

This hash can be loaded into hashcat and possibly cracked (the hash in the screenshot is weak on purpose) Read more “Hacking Guide – AESREPRoast and Kerberoasting” →

PetitPotam Guides

From Zero to DA using ‘PetitPotam’

Introduction

Whilst I was on ‘holiday’ (seriously even when on holiday I almost always must do some work!) a few Windows vulnerabilities were published. Great work by Gilles Lionel, Benjamin Delpy and many many others!

Lab Setup

  • A Domain Controller
  • A Separate ADCS Install with Web Enrolment or two DCs one with ADCS installed.
  • A windows Client Device (non-domain joined)
  • An attacker device (I used Kali)

You do not need any domain credentials to conduct this exploit chain, so from a network adjacent unauthenticated position you can get DA with the right circumstances (default configuration). Read more “From Zero to DA using ‘PetitPotam’” →

Defense

Modern Workspace: PowerShell OAuth Error

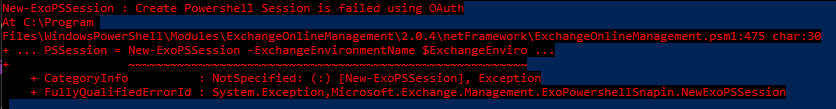
Create PowerShell Session is failed using OAuth

When connecting to Exchange online (there was a reason I needed to do this) I had the following error:

I did some googling that luckily someone has already posted how to fix this:

https://www.vansurksum.com/2021/03/11/create-powershell-session-is-failed-using-oauth-when-using-the-exchange-online-v2-powershell-module/

It turns out WINRM’s ability to use BASIC client authentication is disabled as part of the standard Windows 10 hardening baseline deployed via Intune.

To fix these we need to re-enable BASIC client side WINRM authentication. Read more “Modern Workspace: PowerShell OAuth Error” →

CTF

How to enable NULL Bind on LDAP with Windows…

History of NULL bind

Back in the early Active Directory days NULL bind was actually enabled by default, these days you can get a rootDSE NULL bind out of the box but on Windows Server 2019 you can even disable this!

So why would I want to enable NULL bind? Well, some legacy apps may need it but generally speaking you don’t want NULL bind enabled.

The lesson here is DO NOT copy what I am doing here! Simples! Read more “How to enable NULL Bind on LDAP with Windows Server 2019” →

Defense

Threat Modelling 101

What is a threat?

https://csrc.nist.gov/glossary/term/threat

According to those clever people at NIST it is:

“Any circumstance or event with the potential to adversely impact organizational operations (including mission, functions, image, or reputation), organizational assets, or individuals through an information system via unauthorized access, destruction, disclosure, modification of information, and/or denial of service. Also, the potential for a threat-source to successfully exploit a particular information system vulnerability.” Read more “Threat Modelling 101” →

Defense

CyberChef Taster

A quick snack

Everyone knows about cyber chef, right? Well, I can tell you now that my misses knows so if you don’t now’s a great time to get to know! Cyber Chef is a tool created by GCHQ distrubted via an apache license that’s hosted on GitHub or you can download and run locally. Read more “CyberChef Taster” →